Upload date
All time
Last hour
Today
This week
This month
This year
Type
All
Video
Channel
Playlist
Movie
Duration
Short (< 4 minutes)
Medium (4-20 minutes)
Long (> 20 minutes)
Sort by
Relevance
Rating
View count
Features
HD
Subtitles/CC
Creative Commons
3D
Live
4K
360°
VR180
HDR
413,610 results
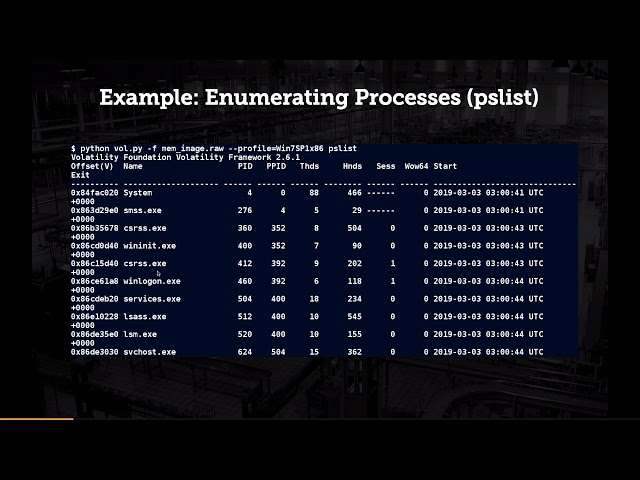
This presentation mainly focuses on the practical concept of memory forensics and shows how to use memory forensics to detect, ...
93,206 views
6y ago
Volatility is a very powerful memory forensics tool. It is used to extract information from memory images (memory dumps) of ...
103,011 views
4y ago
... like going from a cyber security degree to a job in instant response like memory forensics malware analysis yeah the the biggest ...
45 views
1d ago
Andrew Case Memory forensics, which is the analysis of volatile memory (RAM), has proven itself to be one of the most effective ...
749 views
2y ago
cryptology, #cryptography, #cryptanalysis In this video, you get an introduction to memory forensics. It contains a theoretical part, ...
2,056 views
3y ago
Volatility is an open source memory forensics framework for incident response and malware analysis. In this video, @HackerSploit ...
33,184 views
SANS Incident Response Training Course: http://www.sans.org/course/advanced-computer-forensic-analysis-incident-response ...
57,057 views
11y ago
A recording of the January DFIROnline meetup with Michael Cohen of Google Michael is one of the authors of Volatility and has ...
13,972 views
13y ago
https://jh.live/cysec || Find your next cybersecurity career! CySec Careers is the premiere platform designed to connect candidates ...
78,487 views
SecIC January 2018 Meeting Title: "Memory Forensics with Vol(a|u)tility" Speaker: Matt Brenton - @chupath1ngee Links: GrrCON ...
4,222 views
8y ago
Memory forensics is essential for investigating advanced threats like fileless malware and kernel-level rootkits, yet analyzing raw ...
207 views
4mo ago
What if there was a better way? What if examiners could get to critical data quicker? What if the digital data could inform the ...
6,073 views
An introduction to memory forensics and a sample exercise using Volatility 2.6 to analyze a Windows 10 image. #Forensics ...
92,331 views
9y ago
Null404 user BarrySploit showcases how to conduct memory forensics with Volatility. Join us live at null404.org/join.
660 views
Streamed 2y ago
In this presentation, we present our effort to develop algorithms capable of detecting userland device monitoring malware across ...
6,105 views
The number of cyber-attacks is undoubtedly on the rise targeting government, military, public and private sectors. Most of these ...
4,498 views
Memory forensics is a key component of any incident investigation involving endpoints. It can help determine whether an infection ...
2,509 views
5y ago
Endpoint detection and response (EDR) software has gained significant market share due to its ability to examine system state for ...
11,530 views
1y ago
Show more