ViewTube

ViewTube
Sign inSign upSubscriptions
Filters

Upload date

Type

Duration

Sort by

Features

Reset

276 results

AegisPub
Technical Debt Breeds Vulnerabilities - Comprehensive Overview

In this comprehensive guide, we cover software composition analysis, web application firewall, technical debt and more!

58:32
Technical Debt Breeds Vulnerabilities - Comprehensive Overview

0 views

2d ago

Down the Security Rabbithole Podcast
DtSR Episode 727 - LLMs Are Changing Pen Testing

TL;DR: Phile has been penetration testing for a long time. The difference now is that he's having a much easier time with it thanks ...

29:04
DtSR Episode 727 - LLMs Are Changing Pen Testing

35 views

3d ago

BSides Bristol
How Not to Roll Out a Security Tool: A Tale of Broken PRs and Regret - James

So I bought a software composition analysis tool SCA sea reads the dependencies and tells you which ones have known ...

22:20
How Not to Roll Out a Security Tool: A Tale of Broken PRs and Regret - James

3 views

1d ago

Cybersecurity Explained
How AI Hallucinations Can Sneak Malware Into Your Code

What if the package your AI suggests does not exist—until an attacker publishes it? Explore slopsquatting, the supply-chain risk ...

10:22
How AI Hallucinations Can Sneak Malware Into Your Code

0 views

1d ago

Joshua Moses | Cybertrace Foundation
Closing the Loop: Root Cause, Variant Hunting, Secure SDLC, SCA | Bug Bounty Program Ep 30

... test, and deploy, then vendor management for third-party code using SCA (software composition analysis) to identify vulnerable ...

13:26
Closing the Loop: Root Cause, Variant Hunting, Secure SDLC, SCA | Bug Bounty Program Ep 30

1 view

3d ago

Joshua Moses | Cybertrace Foundation
Bug Bounty Readiness Self-Assessment: Team, Baseline, CVSS, Rewards | Bug Bounty Program Ep 9

Then we cover vulnerability management and setting the baseline, including software composition analysis (SCA), scanning an ...

8:11
Bug Bounty Readiness Self-Assessment: Team, Baseline, CVSS, Rewards | Bug Bounty Program Ep 9

1 view

3d ago

Energy AI by quarantadue AI
Analyzing Nuclear Waste Composition Logic | quarantadue.ai

https://quarantadue.ai/nuclear/software/6.7.2 Analyze Composition for nuclear waste validation and classification. The ...

3:45
Analyzing Nuclear Waste Composition Logic | quarantadue.ai

0 views

6d ago

Jeffy G
LoopCloud 8 : New Features Demo, Review & Tips

Special price on subscriptions for new release, for a limited time. 4 MONTHS FREE! or, 14 day free trial #loopcloud #sample ...

11:56
LoopCloud 8 : New Features Demo, Review & Tips

97 views

8h ago

OWASP Foundation
The Velocity Paradox: Why Slow Is Smooth And Smooth Is Fast In AppSec - Pramod Rana

Managed by the OWASP® Foundation https://owasp.org/

45:53
The Velocity Paradox: Why Slow Is Smooth And Smooth Is Fast In AppSec - Pramod Rana

94 views

1d ago

Joshua Moses | Cybertrace Foundation
Can You Fix It? Remediation Capacity, Noise, SLAs, Root Cause | Bug Bounty Program Ep 7

... an insecure deserialization example, and software composition analysis (SCA) for vulnerable dependencies, because security ...

15:56
Can You Fix It? Remediation Capacity, Noise, SLAs, Root Cause | Bug Bounty Program Ep 7

5 views

2d ago

gwendolyn
How To Study and Replicate ANY Art Style

Try out Refbox: https://refbox.app/gwendolyn and use code: GWENDOLYN for 25% off! In this video, I'll teach you ny easy ...

9:24
How To Study and Replicate ANY Art Style

84,019 views

4d ago

Elio's AI Studio
Why I Don't Watch After Effects Tutorials (I'm 50+ and a Software Engineer)

Seedflows: https://seedflows.ai Join my FREE Community: https://www.skool.com/seedflows-2629 Seedflows Motion Studio ...

9:51
Why I Don't Watch After Effects Tutorials (I'm 50+ and a Software Engineer)

55 views

3d ago

AegisPub
Zero-Day is a Known Unknown to the Vendor, Not the Attacker

In this comprehensive guide, we cover defense in depth, indicator of compromise, software composition analysis and more!

1:10:08
Zero-Day is a Known Unknown to the Vendor, Not the Attacker

0 views

4d ago

Industry Exams Plus
CompTIA CySA+ CS0-004 25-Question Practice Exam #2

Practice 25 CompTIA CySA+ questions with answers and explanations. Pause before each answer, test your knowledge, and ...

27:58
CompTIA CySA+ CS0-004 25-Question Practice Exam #2

3 views

5d ago

OWASP Foundation
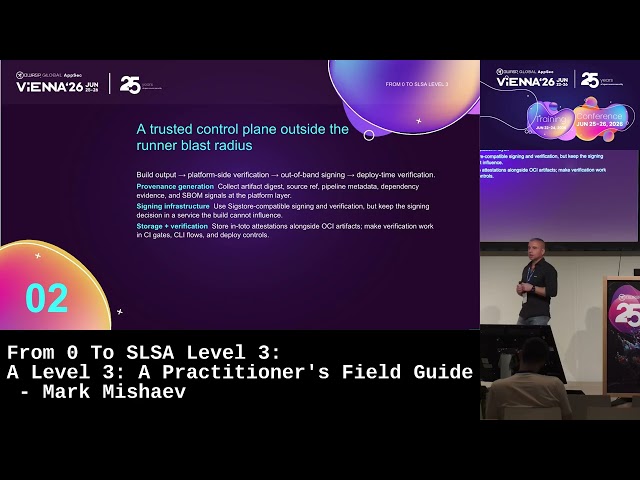
From 0 To SLSA Level 3: A Level 3: A Practitioner's Field Guide - Mark Mishaev

Managed by the OWASP® Foundation https://owasp.org/

36:17
From 0 To SLSA Level 3: A Level 3: A Practitioner's Field Guide - Mark Mishaev

169 views

1d ago

OWASP Foundation
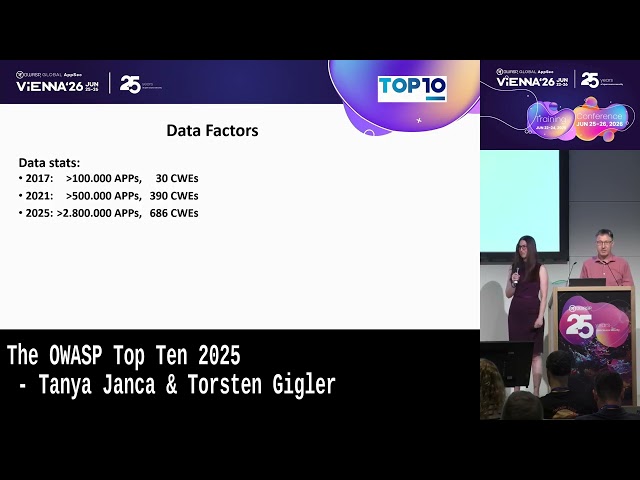
The OWASP Top Ten 2025 - Tanya Janca & Torsten Gigler

Managed by the OWASP® Foundation https://owasp.org/

49:35
The OWASP Top Ten 2025 - Tanya Janca & Torsten Gigler

114 views

1d ago

Industry Exams Plus
CompTIA CySA+ CS0-004 Exam 1 Questions 31-40 | Application Attack Indicators

Build practical CompTIA CySA+ skills with ten original practice questions—not actual exam items—covering application indicators ...

11:31
CompTIA CySA+ CS0-004 Exam 1 Questions 31-40 | Application Attack Indicators

7 views

7d ago

Veo
Veo Analytics 2 and Match Report | Complete Walkthrough for Coaches

A full walkthrough of Veo Analytics 2 and Match Report. See how to find your stats in the Veo Editor, track trends across games in ...

26:48
Veo Analytics 2 and Match Report | Complete Walkthrough for Coaches

702 views

6d ago

Industry Exams Plus
CompTIA CySA+ CS0-004 50-Question Practice Exam #1

Practice 50 CompTIA CySA+ questions with answers and explanations. Pause before each answer, test your knowledge, and ...

54:34
CompTIA CySA+ CS0-004 50-Question Practice Exam #1

32 views

5d ago

VICTOR CHIDI
Domain 8 - CISSP (Certified Information Systems Security Professional)

... Software Composition Analysis (SCA) — Open-source dependency & license scanner - Assessing acquired software: COTS, ...

1:11:05
Domain 8 - CISSP (Certified Information Systems Security Professional)

232 views

Streamed 6d ago