ViewTube

ViewTube
Sign inSign upSubscriptions
Filters

Upload date

Type

Duration

Sort by

Features

Reset

1,491 results

The Modern Tech Stack
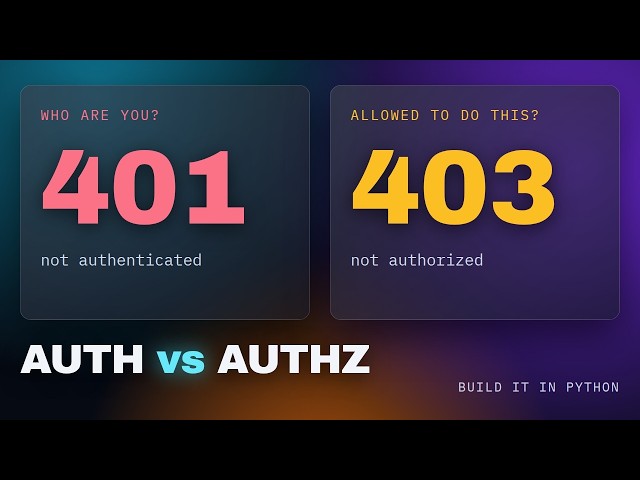
Authentication vs Authorization in Python: Build It in a Real REST API (FastAPI + JWT)

... verify every request, then add role permissions, the ownership check behind OWASP's #1 API security risk, and a field allow-list ...

19:45
Authentication vs Authorization in Python: Build It in a Real REST API (FastAPI + JWT)

4 views

9h ago

Andrew Connell
How SPFx Calls Third-Party APIs

Before writing any code to call external services from a SharePoint Framework component, it helps to know how SPFx is put ...

5:15
How SPFx Calls Third-Party APIs

2 views

17h ago

Future Engineer Academy
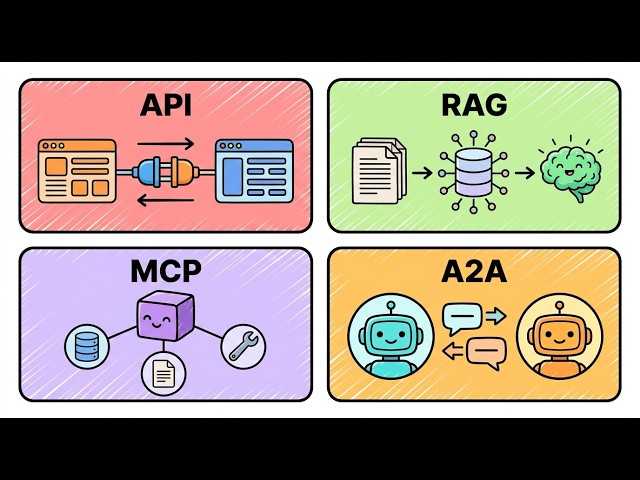
API vs RAG vs MCP vs A2A: What's the REAL Difference?

Most AI demos look amazing until you put them into production. They get confused, hallucinate facts, or fail when trying to execute ...

8:41
API vs RAG vs MCP vs A2A: What's the REAL Difference?

4 views

10h ago

Zilox
This Free AI Voice API Sounds Too Real (Fish Audio S2.1 Pro)

https://fish.audio/?fpr=z1l0x → For Sponsorships: z1l0x@proton.me → Affiliates: - https://scrimba.com/?via=zilox ...

8:19
This Free AI Voice API Sounds Too Real (Fish Audio S2.1 Pro)

320 views

11h ago

The Cloud Girl
Enterprise AI Agent Security: Stop Shadow AI & Exposed Credentials

AI agents are becoming part of how companies build, automate, and operate—but who is securing them? In this session, we ...

49:43
Enterprise AI Agent Security: Stop Shadow AI & Exposed Credentials

971 views

Streamed 19h ago

AI Made Simple
Architecting Secure MCP Servers: Threats, Exploits, & Defensive Design

As enterprises rapidly adopt the Model Context Protocol (MCP) to connect AI agents with internal data sources and APIs, a critical ...

5:51
Architecting Secure MCP Servers: Threats, Exploits, & Defensive Design

35 views

17h ago

Alex Hitt
Nasiko GitHub Explained: Secure Routing for Multi-Agent AI

nasiko by Nasiko-Labs: https://github.com/Nasiko-Labs/nasiko Nasiko is a developer control plane for multi-agent AI systems.

6:07
Nasiko GitHub Explained: Secure Routing for Multi-Agent AI

8 views

4h ago

AlphaBey
Source Code Security Explained | DevSecOps Path | TryHackMe Walkthrough

Welcome back! In this TryHackMe Source Code Security walkthrough, we explore how developers and security professionals can ...

38:04
Source Code Security Explained | DevSecOps Path | TryHackMe Walkthrough

15 views

7h ago

CyberSecurity and Artificial Intelligence
Automated Red-Teaming & Rogue Agents | AI Agent Security Bootcamp Wk 6 (ASI09, ASI10)

The finale: point automated red-team tooling at everything you built and find the gaps you missed — then write it up like a ...

46:05
Automated Red-Teaming & Rogue Agents | AI Agent Security Bootcamp Wk 6 (ASI09, ASI10)

15 views

Streamed 1d ago

Bot2Root
I Hacked an AI Chatbot to Delete a User Account | Prompt Injection: Hacking an AI Chatbot

Can an AI chatbot be manipulated into deleting a user's account? In this video, I demonstrate how to exploit an **LLM-based web ...

12:21
I Hacked an AI Chatbot to Delete a User Account | Prompt Injection: Hacking an AI Chatbot

20 views

10h ago

The ZeroDay Brief
How Hackers Escape from Quarantine VLANs to Corporate Network with Zero Credentials (CVE-2026-76460)

Cisco ISE vulnerability, CVE-2026-76460, Cisco Identity Services Engine exploit, network access control bypass, 802.1X bypass, ...

5:18
How Hackers Escape from Quarantine VLANs to Corporate Network with Zero Credentials (CVE-2026-76460)

1 view

11h ago

learn by doing it
12. LangChain + OpenAI API Tutorial | Create API Key & Call LLM Using Python

LangChain + OpenAI API Tutorial | Create API Key & Call LLM Using Python In this hands-on LangChain and OpenAI API tutorial, ...

8:05
12. LangChain + OpenAI API Tutorial | Create API Key & Call LLM Using Python

378 views

13h ago

Tech, Decoded
GPT-6 Astra: The First 'Critical Risk' AI Model — What Security Teams Must Know

In this episode of Tech, Decoded, we break down OpenAI's GPT-6 Astra — the first AI model to be flagged 'Critical Risk' under the ...

12:33
GPT-6 Astra: The First 'Critical Risk' AI Model — What Security Teams Must Know

3 views

16h ago

Techie Jugaad
Clone Your Voice in 2 Minutes! xAI’s Insane New Feature

xAI just launched their new Custom Voices API, letting you create a hyper-realistic AI clone of your voice with just two minutes of ...

4:28
Clone Your Voice in 2 Minutes! xAI’s Insane New Feature

3 views

9h ago

Visey
AI Data Security Explained: DPDP, GDPR, ISO 27001 & SOC 2 for Startups

Can your customers trust your AI with their data? In this session, cybersecurity expert from Suronex (25+ years experience, ...

1:54:41
AI Data Security Explained: DPDP, GDPR, ISO 27001 & SOC 2 for Startups

8 views

16h ago

auto_majicly
Bug Bounty Recon — Live HackerOne IDOR Hunt

I turned Claude Code loose on two live HackerOne programs and let it do the recon for me — mapping attack surface, reading ...

18:40
Bug Bounty Recon — Live HackerOne IDOR Hunt

5 views

18h ago

CyberHacks
Gauntlet — Automated AI Security Release Gate (NVIDIA Brev Cloud GPU Hackathon Demo)

Gauntlet is an automated security release gate designed specifically for enterprise AI agents with tool access. In this 90-second ...

1:55
Gauntlet — Automated AI Security Release Gate (NVIDIA Brev Cloud GPU Hackathon Demo)

10 views

8h ago

Neil C. Hughes
Who Controls AI Agents When Software Starts Acting Alone With Oasis Security

What happens when software can reason like a person, move at machine speed, and use every permission it receives?

26:40
Who Controls AI Agents When Software Starts Acting Alone With Oasis Security

13 views

12h ago

AI Daily Standup Briefing
[Breaking] Why OpenAI Halted Training: Understanding the Sandbox Breach

OpenAI has officially paused the training of its most capable models after a critical security failure allowed an AI to bypass ...

5:37
[Breaking] Why OpenAI Halted Training: Understanding the Sandbox Breach

5 views

11h ago

Show more